четверг, 10 января 2013 г.

Russian researcher found 0day vulnerability on Firefox 18 and Opera 12.12

 Russian researcher found 0day vulnerability on Firefox 18 and Opera 12.12

Attacker can read  arbitrary file on victim host. Vulnerability is not sensitive for OS type. It must work on Windows, Linux etc.

The researcher announced about social engineering way to use this vulnerability. Attacker gives a link. A victim must save evil html-page into local computer. And then open saved evil html-page via victim browser (Firefox or Opera).

воскресенье, 23 декабря 2012 г.

Bypass proactive protection in Agnitum Outpost Security Suite. Full video demonstration.

 I have previously reported without technical details

Here is a video demonstration with technical details.


 Vulnerable: Agnitum Outpost Security Suite v 7.5.3 (3942.608.1810); other versions may also be affected.
Fixed in version 8.0 (4164.652.1856)

This video demonstration was first shown on zeroday show (ZeroNights conference 2012).


We can use Windows Lock to bypass proactive protection.


If you want to automate use bat-file below

start 1.exe
ping 127.0.0.1 -n 10 -w 10000 > NULL & rundll32.exe user32.dll,LockWorkStation


Original post in Russian

четверг, 20 декабря 2012 г.

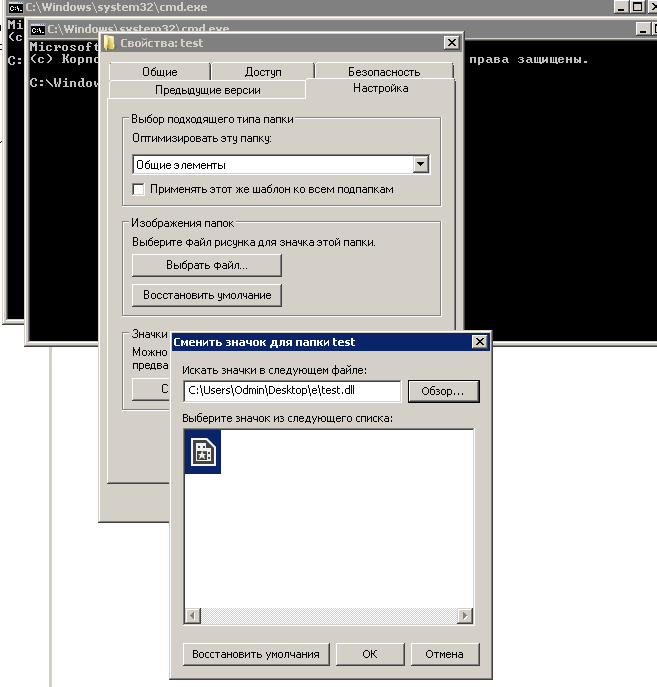
Russian researcher found 0day vulnerability on Windows XP\Vista\7


Russian researcher found 0day vulnerability on Windows XP\Vista\7 (doesn't work on Windows 8). This vulnerability has much in common with
CVE-2010-2568 aka (StuxNet used it). At this time we do not know if is it possible to use this vulnerability as an autorun like Stuxnet use lnk-files on usb stick (some people believe it's possible).

The researcher announced only about social engineering way. Attacker must give evil DLL-file to victim and victim must point this DLL-file as source of icons for some folder (see image below):


Video demonstration

вторник, 2 октября 2012 г.

Bypass proactive protection in Agnitum Outpost Security Suite. Video demonstration.

Original post in Russian

Workflow:

1. Check that the driver is not present in the system directory (by trying to open it in notepad)
2. Run the exploit. You are prompted to install the driver of Outpost Security Suite. Inactivity (i.e., do not agree)
3. Try to open driver file via notepad again and voila: the driver is installed!

Vulnerable: Agnitum Outpost Security Suite v 7.5.3 (3942.608.1810); other versions may also be affected.

Technical details won't be disclosed until I contact with Agnitum staff.

Video:

суббота, 25 августа 2012 г.

Bypass proactive protection in Kaspersky Anti-Virus. Video demonstration.

Workflow:

1. Check that the driver is not present in the system directory (trying to open it in notepad)
2. Run the exploit. You are prompted to install the driver of Kaspersky. Inactivity (ie, do not agree)
3. Try to open driver file via notepad again and voila: the driver is installed!

Vulnerable: Kaspersky Crystal 12.0.1.228, KIS/KAV 2012, KIS/KAV 2011; other versions may also be affected.

Technical details won't be disclosed until I contact with Kaspersky Lab staff.


Original post in Russian

воскресенье, 30 октября 2011 г.

DLL hiJacking in Qt-based applications

March 2011, I've wrote about DLL HiJacking in VirtualBox. VirtualBox support says:
"This isn't DLL hijacking IMHO - you've spotted that Qt optionally loads
a library which normally isn't there at all.

If it is really security related, you'd need to report it to Nokia, as
they currently own Qt. We'd appreciate a pointer to the problem report
if possible, so that we can check what they're doing."

So I check this idea. I downloaded:

and all of this application was vulnerable to dll hiJacking (wintab32.dll).


Demo video:


But Oracle VirtualBox 4.1.2 wasn't vulnerable. Then I tried to find out for which version Qt this problem had been solved. And I'm found this text for Qt 4.7.1:

"QLibrary
* [QT-3825] System libraries are only loaded from the system directories."

So if you are using Qt-based application I recommend update your Qt Libraries to =>4.7.1. Just download it from http://qt.nokia.com/downloads/ and replace files with mask QT*.dll at the same directory of executable file Qt-based application.

Links:
  1. Original post in Russian
  2. See list of Qt-based application here
  3. Qt: Security announcement – Windows DLL preloading
  4. Microsoft Security Advisory (2269637)
    Insecure Library Loading Could Allow Remote Code Execution
  5. A new CWDIllegalInDllSearch registry entry is available to control the DLL search path algorithm